
Pull to refresh
Logo
Let's Encrypt cuts default certificate lifetime to 64 days

Let's Encrypt cuts default certificate lifetime to 64 days

Rule Changes

First reduction in the CA's history, stepping toward 45-day certificates in 2028

Overview

Updated Nov 1

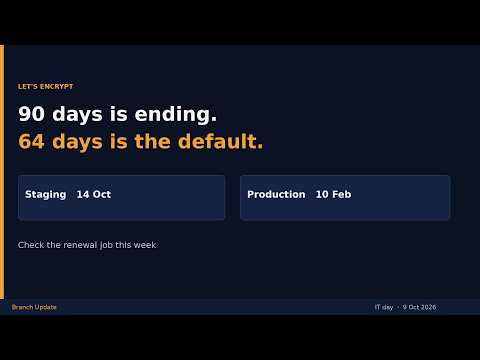
Let's Encrypt will cut its default certificate lifetime from 90 days to 64 days starting February 10, 2027. It's the first reduction in the nonprofit certificate authority's history, and a step toward 45-day certificates in 2028.

The staging environment switched to 64-day certificates on October 14, 2026. Early tests of five ACME clients found most renew on time, but older versions of acme.sh default to a 60-day interval that would renew too late.

Why it matters

Websites that don't automate certificate renewal will need to renew more often, and hard-coded renewal schedules will break.

Questions about this story

Free account needed to ask — your question is kept and asked for you right after sign-up. Answers are public.

No questions yet — be the first to ask.

Key Indicators

64 days
New default certificate lifetime
Down from 90 days, starting February 10, 2027.
45 days
2028 default lifetime
Planned default starting February 16, 2028.
10 days
Authorization reuse period
Down from 30 days, starting February 10, 2027.
90 days
Current default lifetime
The standard since Let's Encrypt launched in 2015.

Voices

Curated perspectives — historical figures and your fellow readers.

Sign up to generate historical perspectives on this story.

Organizations Involved

Timeline

December 2015 February 2028

10 events Latest: October 14th, 2026 · 4 weeks ago
Tap a bar to jump to that date
  1. Default drops to 45 days

    Upcoming Policy Change

    Let's Encrypt's default lifetime is planned to fall to 45 days.

  2. Last 90-day certificate expires

    Upcoming Milestone

    Let's Encrypt expects the final 90-day certificate to expire, completing the transition to 64-day lifetimes.

  3. CA/Browser Forum maximum drops to 100 days

    Upcoming Regulation

    The Forum's ceiling on certificate lifetime falls to 100 days for all publicly trusted CAs.

  4. Production default drops to 64 days

    Upcoming Policy Change

    All new and renewed certificates get 64-day lifetimes. Authorization reuse drops from 30 days to 10 days.

  5. Staging starts issuing 64-day certificates

    Latest Testing

    Let's Encrypt's staging environment began issuing 64-day certificates, confirming the switch from 90-day certificates.

  6. ACME client tests show mixed readiness for 64-day renewals

    Testing

    Tests of five ACME clients against staging certificates found certbot 5.8, acme.sh 3.1.6, and lego 5.5.2 renew within the ARI window. Older acme.sh versions default to 60 days, which would renew too late on 64-day certificates.

  7. Let's Encrypt announces 64-day default

    Announcement

    Let's Encrypt says all certificates issued on or after February 10, 2027 will have 64-day lifetimes by default.

  8. CA/Browser Forum caps lifetime at 200 days

    Regulation

    Ballot SC-081 takes effect, setting the maximum certificate lifetime at 200 days for all publicly trusted CAs.

  9. Let's Encrypt reveals 45-day plan

    Announcement

    Let's Encrypt announces its planned timeline for switching to 45-day certificates, citing CA/Browser Forum requirements.

  10. Let's Encrypt launches public beta

    Launch

    Let's Encrypt begins issuing free certificates with 90-day lifetimes, when three-year certificates were the norm.

Scenarios

1

Automated renewals carry the transition

Likely Resolves by May 11, 2027

Discussed by: Let's Encrypt, Ars Technica

Most renewals run through ACME clients, and clients supporting ARI (ACME Renewal Information) will renew when Let's Encrypt tells them to. Fixed schedules renewing at 60 days will still catch 64-day certificates before expiry. Let's Encrypt expects a smooth transition and says rate limits and issuance chains are unaffected.

2

Hard-coded renewal schedules miss the window

Possible Resolves by May 11, 2027

Discussed by: Scott Helme, SXZ.io

Renewals hardcoded to run at 60 days before expiry will still catch 64-day certificates. Schedules renewing at 80 or 83 days will miss. Let's Encrypt recommends grepping for hardcoded numbers like 83, 80, and 60 in cron jobs and runbooks, and renewing at roughly two-thirds of the lifetime, or 42 days for 64-day certificates.

3

45-day default arrives on schedule in 2028

Likely Resolves by Feb 16, 2028

Discussed by: Let's Encrypt, SecurityWeek

Let's Encrypt has committed to a 45-day default on February 16, 2028, ahead of the CA/Browser Forum's 47-day ceiling in March 2029. Authorization reuse drops to 7 hours at the same time. The 64-day step is designed to ease subscribers into this shorter cadence.

4

Older ACME clients miss the renewal window

Possible

Discussed by: DevOps Daily testing

Tests found acme.sh versions 3.0.7 through 3.1.2 default to a 60-day renewal interval, which would renew at day 59 of a 64-day certificate - only 5 days before expiry. Certbot 2.9, the version on Ubuntu 24.04, renews early but safely. Users on older clients need to update or configure explicit renewal timing.

Historical Context

2 moments from history that rhyme with this story — and how they unfolded.

December 2015

Let's Encrypt launches with 90-day certificates (2015)

Let's Encrypt launched its public beta in December 2015, issuing free certificates valid for 90 days. Commercial certificates at the time commonly lasted three years.

Then

The 90-day lifetime became the norm for automated certificate management.

Now

It proved short lifetimes with automated renewal could work at scale, setting the stage for further cuts.

Why this matters now

The 64-day change is the first reduction to that 90-day default, applying the same logic: shorter lifetimes limit the damage of key compromise.

2025

CA/Browser Forum certificate lifetime reduction (2025)

The CA/Browser Forum set a schedule to reduce the maximum certificate lifetime for publicly trusted CAs over the next several years, with further reductions planned through 2029.

Then

All publicly trusted certificate authorities must comply with the new ceilings.

Now

The industry is moving toward much shorter certificate lifetimes across the board.

Why this matters now

Let's Encrypt's 64-day step is voluntary and ahead of the Forum's schedule, but it's part of the same industry-wide shift.

Sources

(14)