Linux kernel patches 11-year-old TCP bug after Claude writes a root exploit
New Capabilities
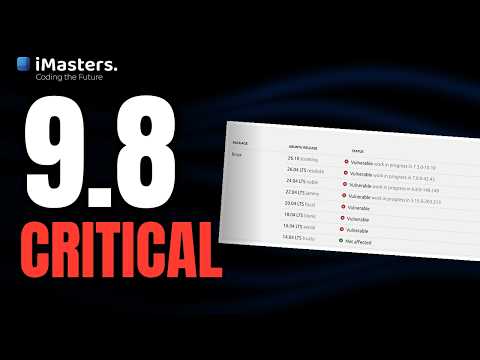
CVE-2026-98432 is a use-after-free in IPv4 TCP options; remote root has been demonstrated against Multipath TCP servers, and Red Hat has shipped fixes while Ubuntu's remain in testing.
Linux kernels have carried a race condition in their IPv4 TCP code since October 2015, when the faulty commit landed for version 4.4. The kernel's CVE team published it as CVE-2026-98432 on October 15, scoring it 9.8 out of 10.
Anthropic says an unreleased Claude model wrote a working exploit that reached remote root in 53 minutes on a server with a Multipath TCP listener. Red Hat shipped fixed RHEL kernels on November 1; Canonical's Ubuntu fixes remained in an opt-in testing channel on November 9. No working remote-code-execution exploit had been published as of November 4, and CISA had not listed the flaw as exploited.
Why it matters
Any Linux server taking IPv4 connections from untrusted networks needs the patch and a reboot, whether or not it enables Multipath TCP.
Questions about this story
Free account needed to ask — your question is kept and asked for you right after sign-up. Answers are public.
No questions yet — be the first to ask.
Key Indicators
9.8
Kernel team CVSS score
The Linux kernel CVE team rated the flaw 9.8 out of 10, citing low attack complexity.
Critical
Red Hat rating
Red Hat raised its rating to Critical and shipped fixed RHEL kernels on November 1.
11 years
Time the flaw went undetected
The faulty commit entered the kernel on October 2, 2015.
53 min
Claude's time to remote root
Anthropic says an unreleased Claude model wrote a working exploit in under an hour.
14 events
Latest: November 2nd, 2026 · 1 week ago
Showing 8 of 14
JK to step
Tap a bar to jump to that date
Jump to
November 2026
Canonical puts Ubuntu kernel fixes in -proposed
LatestDistribution
Canonical said fixes for Ubuntu 22.04, 24.04 and 26.04 were in the opt-in -proposed channel. No regular update date was given.
AlmaLinux moves fixes to production repositories
Distribution
AlmaLinux said the patched kernels were in regular updates for AlmaLinux 8, 9 and 10, no longer needing the testing repo.
Red Hat ships fixed RHEL kernels
Distribution
Red Hat released RHSA-2026:93414, RHSA-2026:93412 and RHSA-2026:93413 for RHEL 8, 9 and 10. A reboot is required.
October 2026
init_on_free=1 floated as interim mitigation
Mitigation
An oss-security post suggests zeroing freed memory to narrow what a use-after-free read exposes.
Public proof-of-concept repositories appear
Exploit
Atlas Security counted at least six public GitHub repositories claiming a race trigger or proof of concept. The flaw was still absent from CISA's catalog.
AlmaLinux ships patched kernels in testing
Distribution
The advisory recommends an nftables rule dropping inbound TCP with IPv4 options.
Red Hat raises rating to Critical
Scoring
Red Hat raised its rating for the flaw to Critical. It shipped fixed RHEL kernels on November 1.
AWS releases patched Amazon Linux kernels
Distribution
Amazon released fixed kernels for Amazon Linux 2 and Amazon Linux 2023. AWS scheduled Redshift, RDS and Aurora patches for November 2 and 3.
LND disables MPTCP listeners by default
Mitigation
LND v0.20.7-beta and v0.21.6-beta turned off Multipath TCP listeners by default, closing the demonstrated route through Bitcoin Lightning nodes. The kernel flaw remains.
NVD still lists 9.8; CISA catalog omits the flaw
Scoring
Red Hat's split between Moderate 5.9 and Important 8.1 is also reported that day.
Anthropic says Claude wrote a working root exploit
Research disclosure
The company reports 48 minutes to leak a kernel address and five more to run commands as root.
Kernel CVE team publishes CVE-2026-98432
Disclosure
The announcement assigns a 9.8 score and lists fixes in 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.56, 7.2.10 and 7.3.
Stable kernels ship the kfree_rcu fix
Fix
Stable kernel releases carrying the fix appeared between October 11 and 18. The change replaces two plain frees with kfree_rcu().
October 2015
Faulty TCP code enters Linux 4.4
Origin
Commit 079096f103fa installs syn_recv request sockets in the ehash table without the listener lock.
Scenarios
1
No public exploit lands and patching completes quietly
Likely
Resolves by Apr 30, 2027
Discussed by: Linux kernel CVE team and AlmaLinux advisories, which both urge patching rather than exploitation watches
Distributions backport the kfree_rcu fix to supported kernels, administrators apply them or the nftables filter, and no confirmed attack appears. The 9.8 score draws attention but the race remains hard to win without the Multipath TCP setup Anthropic used.
2
CISA adds the flaw to its exploited-vulnerabilities catalog
Possible
Resolves by Apr 30, 2027
Discussed by: Security researchers tracking the Anthropic exploit and the gap between kernel and vendor severity scores
A working exploit circulates or attackers reproduce the race against Multipath TCP listeners, giving CISA evidence of use in the wild. Listing in the catalog would trigger patching deadlines for US federal agencies and raise pressure on slower distributors.
3
A weaponized exploit module ships in Metasploit
Possible
Resolves by Apr 30, 2027
Discussed by: Penetration testers and exploit developers following Anthropic's write-up
Anthropic described the exploit but did not publish code. If independent researchers rebuild it and merge a module into a common exploitation framework, attacks become scripted and the pool of capable attackers widens beyond kernel specialists.
4
Ubuntu and Red Hat ship fixed kernels within two weeks
Likely
Resolves by Nov 15, 2026
Discussed by: Ubuntu and Red Hat CVE trackers, which list work in progress
Both vendors have said they are working on fixes. A fixed Ubuntu or RHEL kernel would close the largest remaining gap among major distributions.
5
Ubuntu promotes LTS kernel fixes to regular updates by November 30
Likely
Resolves by Nov 30, 2026
Discussed by: Canonical's security tracker and Ubuntu advisory
Canonical has put fixes for Ubuntu 22.04 and 24.04 LTS in the -proposed channel. The tracker still lists both as vulnerable with work in progress. A move to -updates or -security would make the fix available without opt-in testing.
Historical Context
3 moments from history that rhyme with this story — and how they unfolded.
1 of 3
October 2016
Dirty COW (2016)
A race condition in the Linux kernel's copy-on-write memory handling let any local user gain root. It had existed since 2007, and researchers disclosed it with a working exploit and patches in October 2016.
Then
Distributions shipped emergency kernel updates within days.
Now
It became a reference case for how long kernel race conditions can hide and how fast major distributions can patch when pressed.
Why this matters now
Dirty COW was also an old race condition in core kernel memory handling, disclosed with a proof of concept. It shows how a fix can arrive years after the code does.
2 of 3
April 2014
Heartbleed (2014)
A buffer over-read in OpenSSL's heartbeat extension let attackers read adjacent memory from servers. It was assigned CVE-2014-0160 and disclosed alongside a fix in April 2014.
Then
Large numbers of servers needed certificate and software replacement, and the bug drove a broad audit of OpenSSL.
Now
It pushed memory-safety bugs in core network libraries into mainstream security planning.
Why this matters now
Heartbleed was a memory-safety flaw in widely deployed network code, reachable before applications act. CVE-2026-98432 has the same shape: a stale or out-of-bounds read in software almost every server runs.
3 of 3
March-May 2017
EternalBlue and WannaCry (2017)
Microsoft patched a remote Windows SMB flaw in March 2017. An exploit leaked in April, and the WannaCry ransomware used it in May to spread across unpatched machines.
Then
Hundreds of thousands of computers were affected across more than 150 countries.
Now
It became the standard example of patching lag turning a known flaw into a global incident.
Why this matters now
CVE-2026-98432 has a fix and a public description but no published exploit code. EternalBlue shows what happens when the gap between patch and deployment stays open.