PHP vulnerabilities exploited as websites worldwide go offline
New Capabilities
Palo Alto Networks confirmed the chained PHP2Shell and Fragnesia attack on its firewalls and shipped PAN-OS hotfixes, while Defiant reported 77,000 exploit requests against WordPress and no compromised site
Palo Alto Networks confirmed that attackers chained the PHP2Shell flaws with a Linux kernel bug to take root control of its firewalls, and shipped hotfixes for PAN-OS 12.2, 12.1, 11.2, 11.1 and 10.2. Unit 42, the company's threat research arm, said it independently verified the tooling and results that Dream Security described.
Dream Security's report says attackers rooted 24 firewalls, then an internal firewall-management server, three of them in a US government-affiliated network. Palo Alto says about 0.02% of its installed base had management interfaces reachable from the internet and that it contacted each affected customer. Defiant, meanwhile, says the same exploits are largely failing against WordPress: more than 77,000 requests from over 2,000 IP addresses as of October 28, with no site compromised.
Why it matters
Internet-facing firewalls and web servers can be taken over completely by chaining a PHP flaw with a Linux kernel bug.
Questions about this story
Free account needed to ask — your question is kept and asked for you right after sign-up. Answers are public.
Who first discovered this vulnerability and is there a PHP fix for it already?
N
Calif, working with OpenAI’s AI tools under the Patch the Planet program, was first to report the PHP2Shell flaw, with Wiz Research finding the bugs independently — and PHP has already shipped fixes.
Patch adoption is dangerously slow — about 4% of systems by Oct. 22 — while exploit attempts had already reached millions on Cloudflare’s network.
4 details5 sources2 disagreements
—Calif, an AI-assisted security firm, reported the first flaw to PHP maintainers in August under OpenAI’s Patch the Planet initiative; Wiz says it independently discovered the first vulnerability on Aug. 19 using its own AI stack.
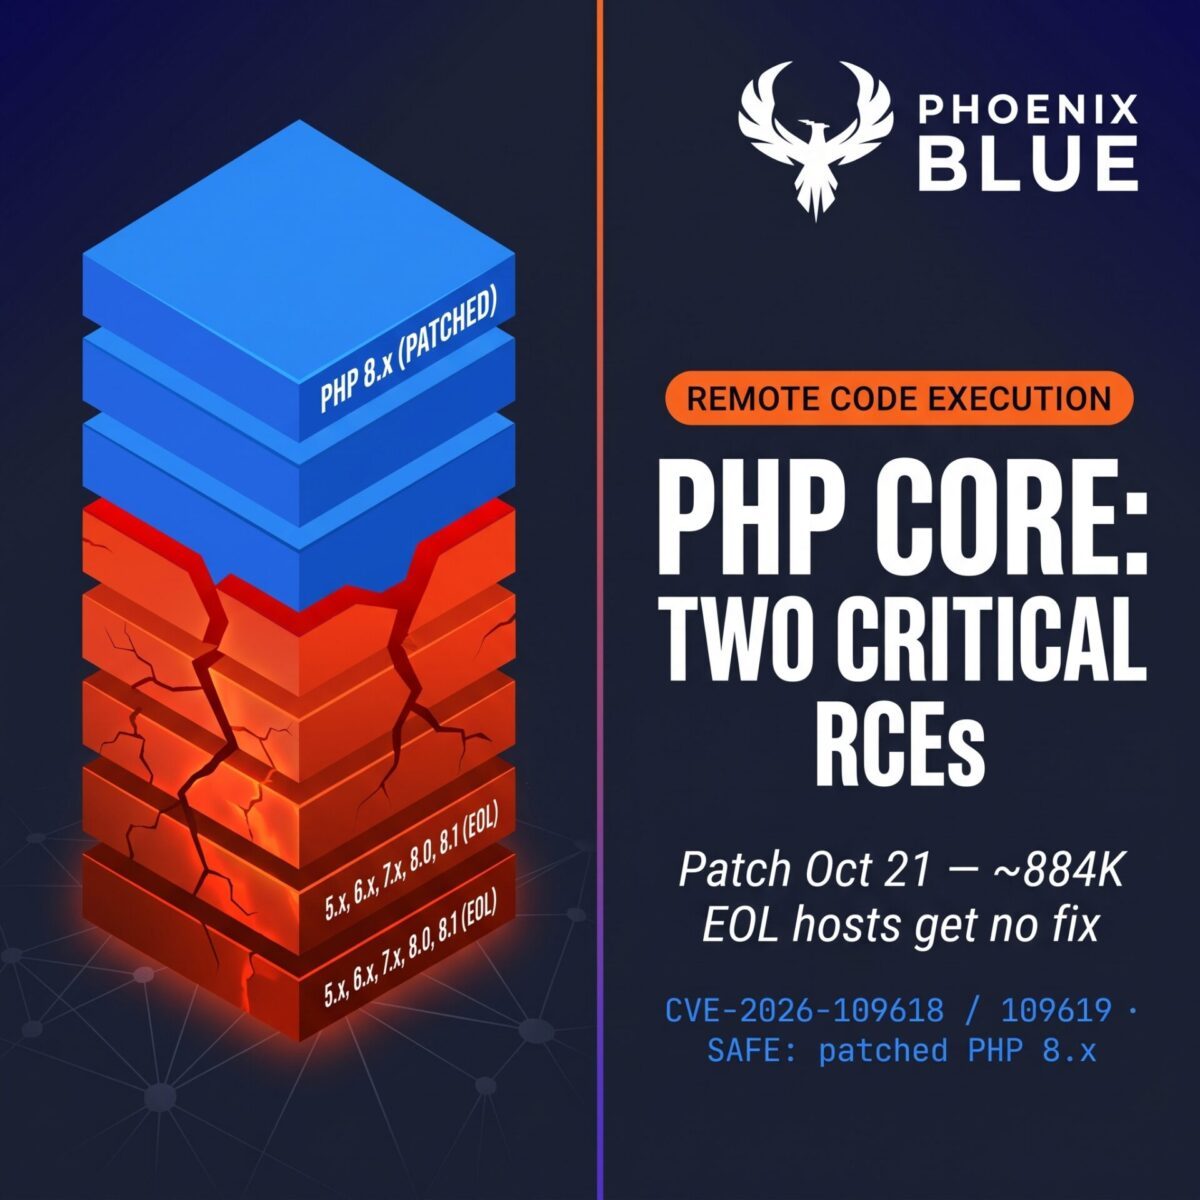
—PHP released patched versions Oct. 21: 8.5.12, 8.4.27, 8.3.36 and 8.2.35, fixing CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on CVSS v4.
—Minimal source backports for the older, unsupported PHP 7.4, 8.0 and 8.1 were also published.
—Amazon says attempts to exploit the flaws began Oct. 17, four days before patches, and the bugs are now being broadly exploited in the wild.
Exactly who gets 'first' credit depends on the source: PHP’s record credits Calif/OpenAI’s August report, while Wiz highlights its own independent Aug. 19 discovery and says it had already confirmed RCE against WordPress and Drupal.
There is also disagreement on impact so far: the PHP Foundation says it knows of no successful remote code execution, while Amazon warns the flaws are now broadly exploited in the wild.
What are some of the most notable hacks that have happened due to this?
N
No confirmed successful hacks have been publicly tied to PHP2Shell so far — the notable incidents are mass exploitation attempts, pre-patch probing, and precautionary website shutdowns.
The distinction matters because the real damage so far is disruption and uncertainty, not proven data theft — but attackers are actively probing and the window for real breaches may still be open.
5 details4 sources2 disagreements
—Amazon Threat Intelligence detected an exploit attempt against one of its decoy systems on October 17, four days before patches shipped, traced to an IP tied to a commercial anonymization network.
—Cloudflare CEO Matthew Prince said the network saw thousands of exploit attempts in the 10 hours before disclosure, tens of thousands within 45 minutes, hundreds of thousands within two hours, and millions by October 22.
—Security firm WatchTowr observed the first in-the-wild exploitation attempts hitting its honeypot sensors around the time patches landed, but said it had not seen any successful attempts; Hadrian separately reported exploitation at scale, mostly abusing PHP's session upload-progress path.
—Governments in Finland, Belgium, the Netherlands, France and Germany, plus the BBC, Edinburgh council and parts of Wikipedia, took websites offline as a precaution; Germany's BSI said it had no reports of successfully compromised federal systems.
—Cloudflare said attackers were already mutating payloads to try to bypass its WAF rules, and Amazon recommended checking for signs of intrusion back to October 17.
Amazon and Hadrian reported active exploitation before or right around patch release, while CISA said it had not observed exploitation as of October 21 and the PHP Foundation said it knew of no successful remote code execution — the gap likely reflects different visibility, not a flat contradiction.
WatchTowr saw in-the-wild attempts but no successes, while Hadrian said PHP2Shell was already being exploited at scale; both could be true if the attacks were noisy and mostly unsuccessful.
0AI answers with web search. May be wrong.
Key Indicators
25
Servers rooted in chained campaign
Dream Security says the attacker rooted 24 PAN-OS firewalls plus an internal firewall-management server, three in a US government-affiliated network.
0.02%
Palo Alto installed base exposed
Palo Alto Networks says about 0.02% of its global installed base had internet-facing management interfaces, and that it contacted each affected customer.
77,000+
PHP2Shell requests against WordPress
Defiant recorded more than 77,000 related requests from over 2,000 IP addresses as of October 28, with no WordPress site compromised.
6+
Successful exploits seen by GreyNoise
The security firm said it had seen at least six successful exploitations of the two PHP flaws.
70%
Estimated share of internet affected
Wiz Research estimates PHP powers 70% of all websites; the BBC could not verify the figure.
9.2
Severity score, out of 10
Palo Alto's advisories rate both PHP2Shell flaws 9.2 under CVSS 4.0.
2
Critical PHP vulnerabilities disclosed
CVE-2026-109618 and CVE-2026-109619, nicknamed PHP2Shell.
Oct 31
Fragnesia federal patch deadline
CISA added CVE-2026-46300 to its exploited-vulnerabilities catalog on October 28 and gave agencies until Saturday, October 31, to patch.
Millions
Exploit attempts on Cloudflare
Cloudflare chief executive Matthew Prince said attempts rose from thousands before disclosure to millions by Thursday, October 22.
5.1 million
PHP hosts exposed online
VirusTotal estimates about 3.8 million of them have at least one port open to attack.
4.21%
Global systems patched
Patch tracking reported by the BBC as of October 22; no newer global figure has been published.
200+
Proof-of-concept exploit samples
Palo Alto Networks' Unit 42 said it was investigating more than 200 pieces of code claiming to exploit the flaws, as of October 22.
32
UK government services offline
Tech minister Baroness Lloyd of Effra told the House of Lords that 32 government services were unavailable and four partially unavailable, mostly as a precaution.
28 events
Latest: October 30th, 2026 · 1 week ago
Showing 8 of 28
JK to step
Tap a bar to jump to that date
October 2026
Palo Alto Networks confirms firewall campaign and details hotfixes
LatestExploitation
Palo Alto Networks said hotfixes for PAN-OS 12.2, 12.1, 11.2, 11.1 and 10.2 fix the PHP2Shell flaws, and its advisory lists exploit maturity as 'ATTACKED'. The company said about 0.02% of its installed base had internet-facing management interfaces and that it contacted each affected customer.
Defiant says PHP2Shell exploits fail against WordPress
Exploitation
Defiant said it knew of no WordPress site compromised through PHP2Shell as of October 28, despite more than 77,000 related requests from over 2,000 IP addresses. The firm said exploits often need adjusting for address randomization, the PHP build, running extensions and memory limits.
Dream Security reports firewalls rooted with chained exploits
Exploitation
Dream Security said an attacker exploited the PAN-OS management web server with a custom PHP2Shell exploit, then chained it with Fragnesia to root 24 firewalls and an internal firewall-management server in the US, Japan, Taiwan and South Korea. Dream dates the first firewall compromise to October 23 and says 22 firewalls were left with webshells. Palo Alto's Unit 42 verified the tooling and results, and Palo Alto shipped PAN-OS hotfixes.
GreyNoise counts at least six successful PHP2Shell exploits
Exploitation
Cybersecurity firm GreyNoise said it had seen at least six successful exploitations of CVE-2026-109618 and CVE-2026-109619.
CISA adds Fragnesia kernel bug to exploited list
Response
CISA added CVE-2026-46300, a Linux kernel privilege escalation bug called Fragnesia, to its Known Exploited Vulnerabilities catalog and told federal agencies to patch by Saturday. The agency said it can be chained with the PHP flaws to plant webshells and run commands as root.
CISA lists PHP2Shell as exploited and sets Thursday deadline
Response
CISA added CVE-2026-109618 and CVE-2026-109619 to its Known Exploited Vulnerabilities catalog and ordered federal civilian agencies to patch by October 29 under Binding Operational Directive 26-04.
Researcher confirms working PHP2Shell exploits on honeypots
Exploitation
Adel Karimi, detection and response lead at Perplexity, published an analysis over the weekend documenting 35 shells launched from two IP addresses against three honeypots running Apache mod_php and PHP 8.4.26. He said the attacks produced confirmed remote code execution with a usable memory disclosure, not just a crash.
PHP team publishes workaround for a third flaw
Response
PHP published an informational advisory telling operators to set session.upload_progress.enabled=0 until its next bugfix release. The setting covers CVE-2026-115560, a remote code execution flaw with no patch that needs an unusual combination of configuration and application code.
Cloudflare reports millions of exploit attempts
Exploitation
Cloudflare chief executive Matthew Prince said the network saw thousands of attempts in the 10 hours before disclosure, tens of thousands within 45 minutes, hundreds of thousands within two hours, and millions by the next day.
Germany's BSI says no confirmed compromises in federal systems
Response
The Federal Office for Information Security said it had received no reports of successfully compromised federal IT systems and that sites taken down as a precaution were mostly back online. It said successful attacks could not be ruled out.
PHP Foundation says no confirmed remote code execution
Response
Executive director Elizabeth Barron told WIRED the foundation was unaware of Amazon's pre-patch research and said, 'to our knowledge, there has been no successful attempt at remote code execution.'
UK minister says 32 government services taken offline
Response
Tech minister Baroness Lloyd of Effra told the House of Lords that 32 government services were unavailable and four partially unavailable, mostly as a precaution while updates were applied. The National Cyber Security Centre said it sent 50,000 alerts to affected organisations and had no reports of successful hacks.
Japanese banks and airline suspend services
Response
Mizuho's bank and securities arms halted services and Shizuoka Bank suspended its website and app, Bloomberg reported. All Nippon Airways disabled boarding, and companies in the MUFG group halted some online services.
Security firms see scanning but no confirmed compromises
Exploitation
Dataminr's threat research team said observed activity was limited to scanning, fingerprinting and non-working exploits, with no known compromises. A researcher at the security startup Tolmo told CNBC his team had built a working exploit in less than a day.
Nine security firms report no successful attacks
Exploitation
CrowdStrike, ESET, Google Threat Intelligence Group, Huntress, Palo Alto Networks, Recorded Future, SecureWorks, Sophos and Trail of Bits told NBC News they had seen no successful attacks as of Thursday evening. Sophos threat research chief Don Smith said the firm had seen 'only a couple of real exploitation attempts'.
Unit 42 counts more than 200 exploit samples
Exploitation
Palo Alto Networks' Unit 42 said it had collected over 200 pieces of proof-of-concept code claiming to exploit the PHP flaws and was investigating them all. Vice-president Sherrod DeGrippo said the firm had not yet seen the flaws exploited in the wild.
Japan's prime minister urges patching; South Korea raises alert
Response
Sanae Takaichi urged site owners on X to install the fix as soon as it was released. Chief Cabinet Secretary Minoru Kihara said no attacks exploiting the flaws had been confirmed, and South Korea raised its cyber alert level for the private sector.
Cloudflare says no customers affected; UK cyber chief calls response unprecedented
Response
Cloudflare chief executive Matthew Prince said none of the company's customers were affected and that it had been discussing the flaw for months. The NCSC's chief technology officer, Olly Whitehouse, called the event 'unprecedented' and said there were no indications of successful breaches.
Finland's Valtori lifts some service blocks
Response
Finland's state IT provider said it had installed PHP patches overnight and was gradually lifting precautionary blocks on government web services. Director General Hannu Naumanen said restoring services can take days or weeks because systems need testing.
PHP releases patches; governments and companies take sites offline
Response
PHP released patched versions; governments in Finland, Belgium, the Netherlands, France and Germany, the BBC, Edinburgh council and parts of Wikipedia took websites offline as a precaution.
FBI cyber division warns of PHP flaws
Response
The FBI's cyber division warned that the flaws could let attackers run code remotely, and recommended operators take websites offline if they could not update them immediately.
PHP team issues backports for unsupported versions
Response
The PHP security team published minimal source backports for PHP 7.4, 8.0 and 8.1, and said the volunteer-run rpms.remirepo.net repository would not receive updates that day.
NSA issues advisory on PHP vulnerabilities
Response
The NSA urged organizations to inventory PHP systems, apply vendor patches, and take systems offline if they cannot update immediately.
Amazon reports broad exploitation after patch
Exploitation
Amazon said proof-of-concept exploits appeared within hours of the patch and were used against its sensors almost immediately. It recommended checking for signs of intrusion back to October 17.
Linux distributions publish patched PHP packages
Response
Debian packages were available after 9 p.m. on October 21, with Fedora, Ubuntu, Red Hat, Gentoo and Slackware following; SUSE made new packages available later, heise reported.
PHP developers disclose two critical vulnerabilities, urge updates
Disclosure
PHP developers identified two critical vulnerabilities and urged users to update as soon as a fix was released.
Amazon decoy system targeted before PHP patch
Exploitation
Amazon Threat Intelligence said it detected a hacking attempt against one of its decoy systems on October 17, four days before PHP released fixes. Amazon said it was unclear how the actor learned about the flaws.
August 2026
Calif and OpenAI report first PHP flaw to maintainers
Discovery
Security firm Calif, working with OpenAI, reported the first php2shell flaw to PHP maintainers.
Scenarios
1
Patch adoption contains the threat
Likely
Resolves by Nov 21, 2026
Discussed by: CISA and national cybersecurity agencies
Organizations apply the patches released October 21, and internet-facing systems are updated within weeks. The coordinated disclosure, aided by AI-assisted discovery, gives defenders a head start.
2
Exploitation spreads to unpatched servers
Possible
Resolves by Nov 21, 2026
Discussed by: Cloudflare CTO, Wiz Research
Attackers scan the internet for vulnerable PHP versions, targeting the estimated 70% of sites that run PHP. Early attacks were already emerging, according to Cloudflare's chief technology officer.
3
AI-assisted discovery finds more flaws
Possible
Resolves by Jan 21, 2027
Discussed by: OpenAI, Wiz Research
The same AI-assisted techniques that found php2shell uncover additional critical vulnerabilities in PHP or other foundational software. OpenAI's Patch the Planet initiative continues to coordinate disclosures.
4
Sites on PHP 8.1 and older stay exposed
Possible
Resolves by End of 2026
Discussed by: PHP security team
PHP 8.1 and older no longer get updates from the PHP project. The security team released minimal source backports for 7.4, 8.0 and 8.1, but organizations that cannot rebuild from source depend on Linux distributions or paid support vendors for fixes. Those servers can stay vulnerable while patched versions spread across supported installations.
Attackers are scanning for vulnerable PHP versions and using exploit code that appeared within hours of the patch. Amazon said it saw the exploits used against its sensors almost immediately and recommends checking for signs of intrusion back to October 17.
6
Patch rates stay low and exposed servers persist
Likely
Resolves by Nov 30, 2026
Discussed by: BSI, Cloudflare, BBC patch-rate tracking
Only about 4% of systems worldwide had been patched by October 22, and many PHP installs sit inside appliances and hosted services that owners cannot update directly. If the rate stays slow, attackers keep a large pool of vulnerable servers to scan.
7
Working exploit code goes public and mass compromise follows
Possible
Resolves by Nov 30, 2026
Discussed by: Tolmo researcher Matt Suiche, Dataminr threat research team
A Tolmo researcher said his team built a working exploit in under a day, while Dataminr reported that public activity so far is scanning and non-working code. Release of functional exploit code would let attackers without the skill to write their own hit servers that are still unpatched.
8
First confirmed breach surfaces at an unpatched site
Possible
Resolves by Nov 20, 2026
Discussed by: Palo Alto Networks Unit 42, Sophos, Germany's BSI
Researchers now have confirmed exploitation on decoy servers, but no organization has reported a real intrusion. Karimi's honeypots ran a deliberately simple single-worker mod_php setup, so his result does not measure how reliably the chain works elsewhere. A named victim would mark the start of real damage.
9
Working exploits reach production sites, not just honeypots
Possible
Resolves by Nov 30, 2026
Discussed by: Adel Karimi, Marcus Hutchins, CISA
Karimi confirmed shells on decoys he configured himself with a single-worker mod_php setup, and said his evidence does not measure exploit reliability on other worker counts, PHP builds or applications. CISA's catalog listing puts federal systems on a Thursday deadline. A named victim would show the exploit works on ordinary configurations at scale.
10
Chained kernel bug widens the damage beyond web servers
Likely
Resolves by Nov 30, 2026
Discussed by: CISA, Dream Security
Attackers pair the PHP flaws with the Fragnesia Linux kernel bug to get root access on hosts that patched PHP but not their kernels. Dream Security's report already describes this pattern against firewalls, and CISA has put both bugs on its exploited list.
Historical Context
3 moments from history that rhyme with this story — and how they unfolded.
1 of 3
December 2021
Log4Shell (2021)
Researchers disclosed a critical remote code execution vulnerability in Log4j, a Java logging library used by millions of applications. Attackers could exploit it with a single crafted string, and scans for vulnerable systems began within hours.
Then
Organizations scrambled to patch, and the US government ordered federal agencies to fix the flaw within days.
Now
Log4Shell became a benchmark for critical software supply chain vulnerabilities, prompting new scrutiny of open-source dependencies.
Why this matters now
Like php2shell, Log4Shell affected a foundational piece of software used across the internet, forcing a global patching effort.
2 of 3
April 2014
Heartbleed (2014)
Researchers disclosed Heartbleed, a memory disclosure bug in OpenSSL, the encryption library used by most of the internet. Attackers could read sensitive data, including passwords and private keys, from vulnerable servers.
Then
Websites and services rushed to patch and revoke certificates, with major platforms updating within days.
Now
Heartbleed led to the creation of the Core Infrastructure Initiative to fund open-source security.
Why this matters now
Heartbleed showed how a single flaw in a widely used open-source component can expose a large share of the internet, a pattern php2shell repeats.
3 of 3
September 2014
Shellshock (2014)
Researchers disclosed Shellshock, a command injection vulnerability in Bash, the Unix shell. It affected millions of servers and devices, allowing remote attackers to execute commands.
Then
Organizations patched rapidly, but the flaw was found in many embedded devices that could not be easily updated.
Now
Shellshock highlighted the difficulty of securing software that is embedded in hardware and legacy systems.
Why this matters now
Shellshock, like php2shell, affected a foundational component of the internet and required urgent, global patching.