
Pull to refresh
Logo
Austin ISD staff social security numbers exposed in data breach

Austin ISD staff social security numbers exposed in data breach

Force in Play Austin, TX local

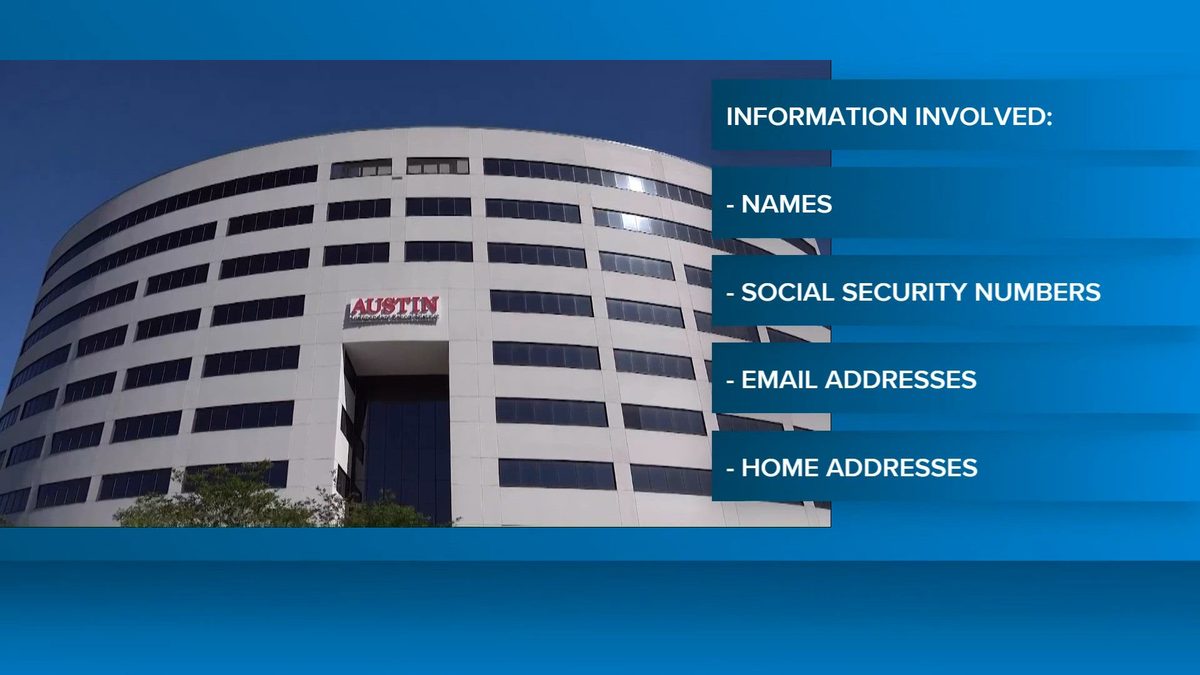
Austin ISD says a Frontline Education software breach exposed staff Social Security numbers, emails and home addresses

Overview

Updated Oct 29

Austin Independent School District told staff on October 26 that a vulnerability in a Frontline Education software product exposed names, Social Security numbers, work and personal email addresses, and home addresses. The district said the flaw was discovered on August 14, reported the incident to the Texas Department of Information Resources, and would provide credit monitoring and identity protection.

Frontline began notifying affected employees across the country on October 26 and offered two years of credit monitoring through TransUnion. Killeen ISD said about 45,000 current and former employees may be affected, and Galveston ISD reported 1,942. Frontline says it knows of no misuse of the data.

Why it matters

Stolen staff social security numbers put Austin ISD employees at lasting risk of identity theft and financial fraud.

Last Monday's email for Austin, TX

Sent Nov 9. It carried:

Get next Monday's: one short email a week. Free. Unsubscribe in one click.

Questions about this story

Free account needed to ask — your question is kept and asked for you right after sign-up. Answers are public.

No questions yet — be the first to ask.

Key Indicators

Frontline Education
Vendor in breach
Austin ISD said a vulnerability in a Frontline Education product exposed staff data.
2026-08-14
Vulnerability found
Frontline says it found the flaw August 14; unauthorized access ended August 15.
45,000
Killeen ISD employees potentially affected
Killeen ISD said Frontline told it about 45,000 current and former employees may be exposed.

Voices

Curated perspectives — historical figures and your fellow readers.

Sign up to generate historical perspectives on this story.

Organizations Involved

Timeline

April 2026 October 2026

10 events Latest: October 28th, 2026 · 2 weeks ago
Tap a bar to jump to that date
  1. San Antonio ISD warns staff of Frontline breach

    Latest Disclosure

    San Antonio ISD told employees that district data was involved in Frontline's breach and that no student records were affected. Affected employees will hear directly from Frontline.

  2. Austin ISD confirms staff data breach tied to Frontline Education

    Disclosure

    The district told staff that a vulnerability in Frontline Education's software exposed names, Social Security numbers, work and personal email addresses, and home addresses. Austin ISD said it reported the incident to the Texas Department of Information Resources and would provide credit monitoring.

  3. Frontline begins notifying affected employees

    Disclosure

    Frontline started sending notices by email and mail and published a breach notice. It offered two years of credit monitoring through TransUnion.

  4. Galveston ISD reports 1,942 employees affected

    Disclosure

    Galveston ISD said the breach involved personal information for 1,942 current and former employees, including Social Security numbers, government IDs, home addresses and email addresses.

  5. Killeen ISD says 45,000 may be affected

    Disclosure

    Killeen ISD said Frontline told it that personal information for about 45,000 current and former employees and others may have been exposed. The district said its own systems were not breached.

  6. Frontline finds vulnerability in third-party software

    Incident

    Frontline Education says a vulnerability in a third-party product let an unauthorized party into part of its systems. The company says the access began August 14 and ended August 15.

  7. Austin ISD suspends BLEND after ShinyHunters claim

    Response

    The district removed platform access after a hacker posted a ransom message on BLEND; services were later restored.

  8. Instructure revises: student data involved

    Update

    The vendor told Austin ISD that student information was affected, after initially saying it was not.

  9. Instructure alerts Austin ISD

    Disclosure

    Instructure notified the district of unauthorized access, initially reporting no impact on student data.

  10. Attacker gains access to Instructure systems

    Incident

    A threat actor gained unauthorized access to Instructure's systems, beginning the incident later disclosed to schools.

Scenarios

1

Austin ISD confirms scope and offers credit monitoring

Likely Resolves by Feb 28, 2027

Discussed by: Austin ISD letter to staff, reported by KVUE

Austin ISD told staff on October 26 which data was exposed and said affected employees would receive credit monitoring and identity protection services.

2

Additional data types or systems found exposed

Possible Resolves by Q1 2027

Discussed by: Frontline's October 26 breach notice and district statements

Austin ISD's notice listed names, Social Security numbers, work and personal emails and home addresses. Across Frontline's customers, the breach also involved dates of birth, driver's license and passport numbers, Medicaid IDs and student IDs.

3

Texas state inquiry opens into the breach

Uncertain Resolves by Q2 2027

Discussed by: Texas data breach notification requirements to the state Attorney General

Texas authorities open an inquiry into whether Austin ISD met its data protection and notification duties. The state Attorney General's office has shown willingness to investigate school district matters, though the record does not confirm it has acted here.

Historical Context

2 moments from history that rhyme with this story — and how they unfolded.

December 2024 – January 2025

PowerSchool data breach (2024-2025)

PowerSchool, a student information system vendor used by thousands of school districts, disclosed that attackers using stolen credentials accessed records of students and staff. In some cases, social security numbers were among the exposed data.

Then

Districts notified families and offered credit monitoring; PowerSchool reportedly paid the threat actor to delete the stolen data.

Now

The breach became a cautionary example of how one education vendor's security lapse can expose records across many districts at once.

Why this matters now

Like the Instructure incident, PowerSchool shows that a single vendor breach can put staff and student data across many districts at risk, the same dynamic now facing Austin ISD.

2015

OPM data breach (2015)

Hackers breached the US Office of Personnel Management, stealing background-investigation records of roughly 22 million current and former federal employees and contractors, including social security numbers.

Then

The government offered affected individuals credit monitoring and launched a review of federal cybersecurity practices.

Now

The breach remains a reference point for the long-lasting identity theft risk that follows social security number exposure.

Why this matters now

OPM demonstrates that once social security numbers are stolen, the fraud risk persists for years, which is the concern Austin ISD staff now face.

Sources

(7)